01
PREVENT
Stop risk before it moves. Inline interception classifies every outbound message, document, and workflow trigger against your policy library in real time.
Prevent risk before it becomes an incident – across email, chat, documents, and workflows, in real time.
Confinaid sits inline – between your employees and their outbound communications, documents, and workflows. It classifies risk, applies policy, and takes action before content leaves your environment.
Stop risk before it moves. Inline interception classifies every outbound message, document, and workflow trigger against your policy library in real time.
Your team decides. Flagged items queue for human review by your compliance team – not Confinaid staff. Confinaid staff have zero access to message content.
Policies get smarter. Analytics surface risk patterns. Policy recommendations adapt to your organization's communication and operational profile. The system learns within your boundary.
Auditable by design. Every action, every decision, every escalation is timestamped and cryptographically logged. When a regulator arrives, your evidence is already organized.
Real-time DLP across all outbound channels – email, chat, documents. Low-latency inline decisioning.
Structured review queue for your compliance team. No Confinaid staff access to message content.
Evidence-based policy Q&A. Every answer grounded in your own documentation and traceable to a source, to minimize hallucination risk.
Risk classification for outbound documents, attachments, and shared files. Beyond email.
Organizational risk score, trend analysis, and compliance reporting dashboards.
Context-aware compliance training triggered by employee risk events. Learning where it matters.
Structured investigation workspace. Virtual raid readiness built in.
One-click activation: retention freeze, heightened monitoring, defensible documentation package.
Customizable rule library, policy versioning, and approval workflows. Your rules, governed by your team.
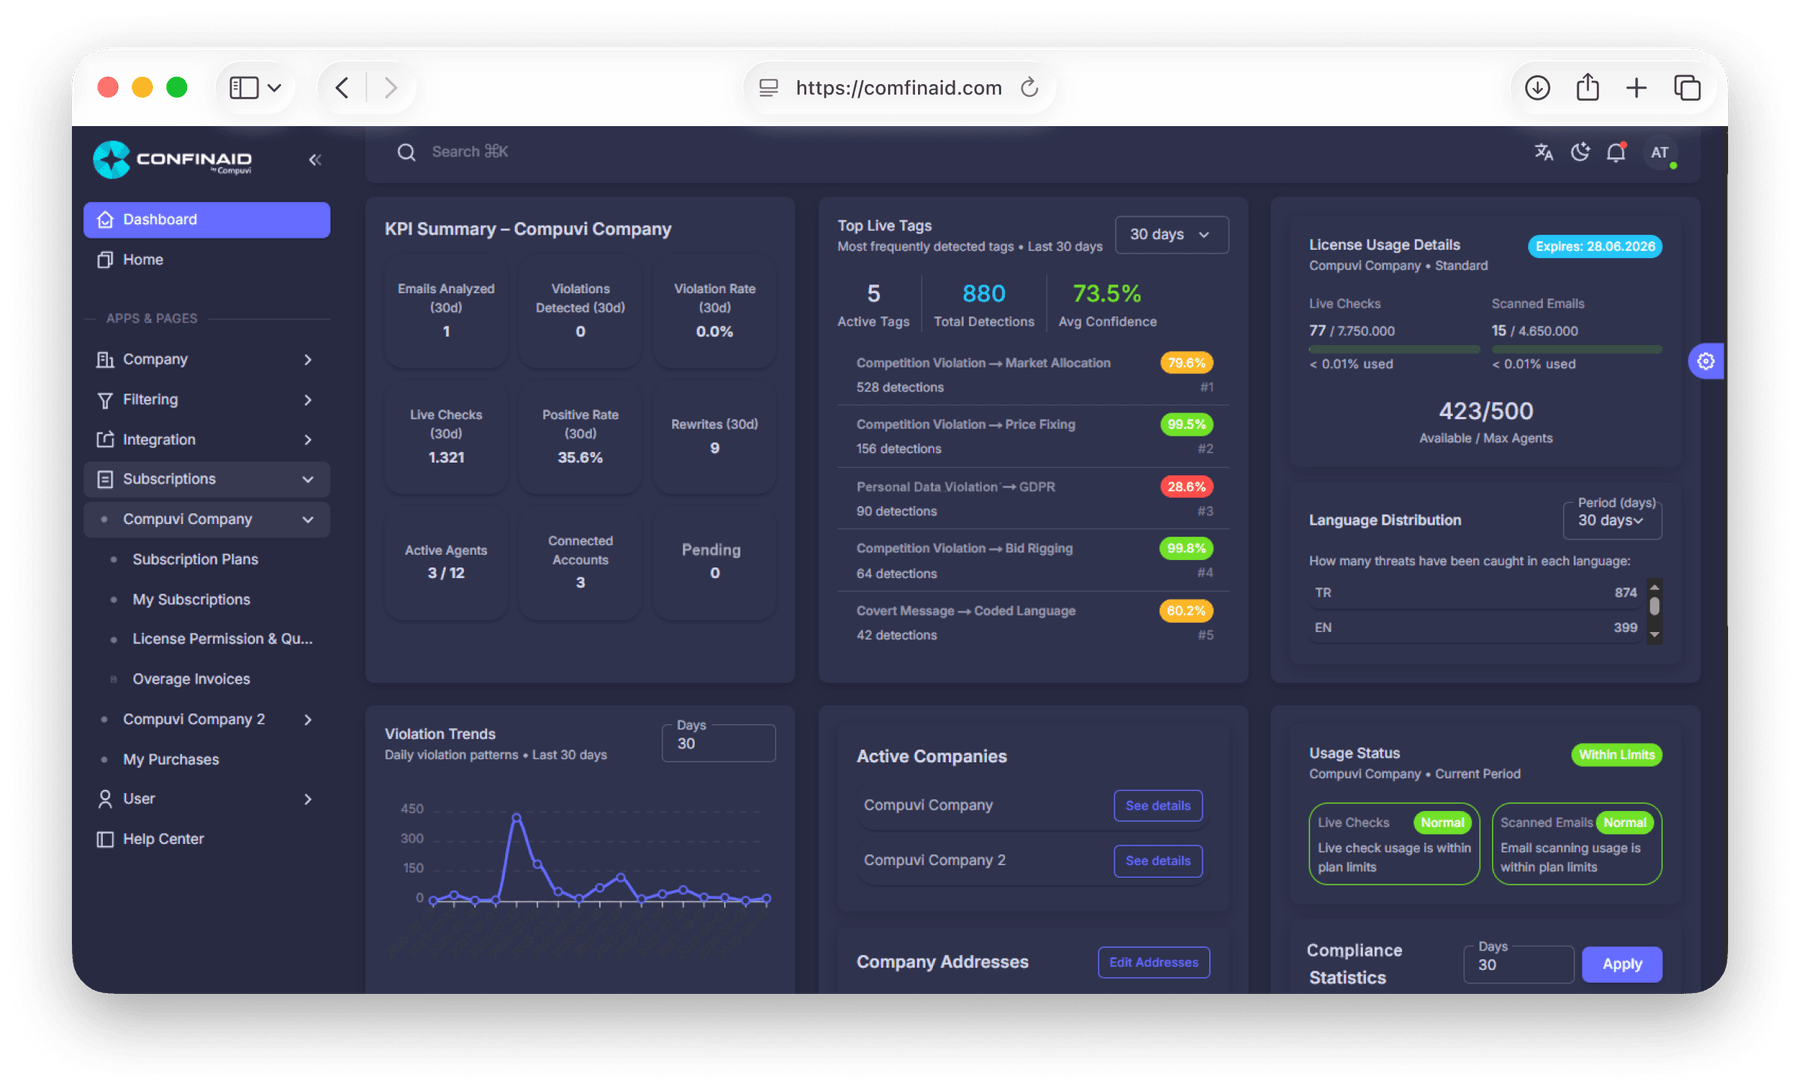
Confinaid provides the workflow – structured queuing, context surfacing, policy references, and audit logging. The review decisions are made exclusively by your own legal and compliance staff
Confinaid doesn't make compliance decisions. It makes compliance decisions possible – faster, with better evidence.
Dawn Raid Mode activates a documented incident protocol – one click, fully auditable. Designed for the moment that every regulated enterprise dreads.
Regulatory access is restricted. All interactions logged.
Confinaid's AI doesn't guess. Every risk classification, policy recommendation, and compliance response references a specific rule, its rationale, and a policy document. This makes it defensible in any regulatory or legal context.
Competitors: generative summaries with no source anchor – a hallucination liability.
Confinaid: every output carries rule ID, policy section, and explainable rationale
API-based integration. No endpoint agents. No email routing changes required. SPF, DKIM, and DMARC records are preserved via re-injection.
Exchange, Teams, SharePoint, OneDrive
Gmail, Drive, Chat, Docs
Channels, DMs, Workflows
Ticket creation, workflow triggers
Transparent about where we are – and where we're going. We don't overclaim certifications we haven't earned.
Every action, decision, and escalation is timestamped and cryptographically logged. Nothing is editable after the fact.
Granular RBAC across all modules. Reviewers, admins, auditors, and investigators have strictly scoped permissions.
Confinaid processes only what is needed for risk classification. Content is not stored beyond policy requirements.
Full deployment within your own infrastructure available. No data leaves your environment – suitable for financial and government clients.
Your data remains yours. Encryption keys, retention policies, and deletion rights are controlled by your organization.
Separation of concerns is enforced at the infrastructure level – not applied as a policy after the fact.
Prevention, review, and proof – in one platform.


 Full capacityPartial / limitedNot available
Pricing is customized by protected users, channels selected, and modules activated.
Core DLP + HITL. Up to 50 protected users. Fixed 60-90 day duration. Full reporting.
Email + Chat. DLP, HITL, Analytics, Policy Management. Ideal for compliance teams.
All channels. Core modules + Document Intelligence + Audit Mode + LMS. Preferred for regulated enterprises.
Full platform. All 9 modules. Multi-tenant, RBAC, SLA guarantees, dedicated CS. On-prem option.
Bespoke deployment for the world's most complex compliance environments. Contact us.
API connections live. Policy library configured. First integrations validated
Your compliance team reviews initial flags. Rules calibrated to your risk tolerance
Measurable risk reductions visible. First audit-ready reports available
Full rollout decision based on pilot data. Procurement documentation complete.
Success criteria and pilot scope are defined together before kickoff. No surprises. No moving goalposts